Threat Intelligence
What Is Port Scanning: How Attackers Map Your Network
Port scanning reveals which services run on your network, allowing attackers to target specific software vulnerabilities instead of guessing blindly.
Everything NetSec Observer has reported about network security: 7 stories, newest first. Part of our Threat Intelligence coverage.
Port scanning reveals which services run on your network, allowing attackers to target specific software vulnerabilities instead of guessing blindly.
IP spoofing fails when network devices verify the source address before accepting the packet, turning a complex attack into a simple routing error.
Server-side request forgery often succeeds because code trusts user-supplied URLs without verifying the destination or restricting outbound network paths.
Reconnaissance is often silent and leaves no obvious traces, so standard alerting fails until the attacker moves laterally or exfiltrates data.
BGP hijacking redirects global internet traffic to unauthorized servers, allowing attackers to intercept data without breaking any encryption keys on your local network.
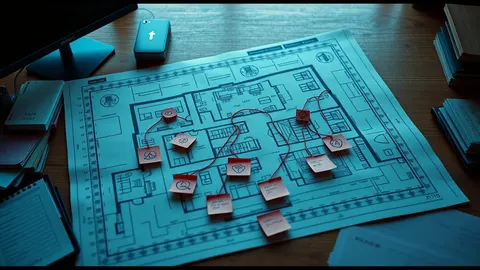
Attackers map your network before attacking, treating your devices like rooms in a house they are planning to break into.
Most defenses fail because they assume the perimeter is the only entry point, leaving internal trust relationships wide open to abuse.