Threat Intelligence
OSINT tools for investigators map digital footprints
Public data collection requires strict verification because threat actors routinely plant fabricated artifacts across indexed web pages.
Reference guides from the NetSec Observer newsroom. They explain the ideas behind the headlines and are reviewed when the facts change.
Public data collection requires strict verification because threat actors routinely plant fabricated artifacts across indexed web pages.
Dark web search engines often index leaked credentials and internal corporate documents long before security teams realize the exposure occurred.
External attack surface scanning reveals hidden digital assets that internal audits miss, exposing the true scope of your organization's exposure to remote threats.
Misconfigured parsers and outdated libraries allow attackers to execute arbitrary code on your server without needing valid credentials.
Zero-click exploits compromise devices without user interaction, making traditional security warnings and training ineffective against silent data theft.
Treating exceptions as permanent fixes creates hidden debt. Proper exception handling requires strict time limits, active monitoring, and compensating controls to keep risk within bounds.
Server-side template injection allows attackers to execute code on your server by manipulating how data is rendered, not just by escaping output.
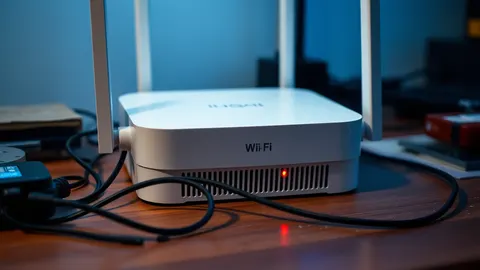
Most router breaches occur because users ignore default settings, leaving hidden management interfaces and outdated code open to public exploitation without any physical access.
Factory software often lacks modern security because speed and uptime matter more than encryption in these critical physical systems.
Hardcoded secrets leak when developers commit credentials to version control, creating permanent exposure even after the code is deleted from the repository history.
CSAF replaces human-readable PDFs with machine-readable JSON that tracks affected products and fixes with precise structural detail.
Attackers exploit misconfigured local accounts and unpatched services to gain administrative control, turning a simple malware infection into total system compromise.
Python pickle executes arbitrary code during deserialization, turning trusted data sources into direct paths for remote code execution on your server.
Scanning infrastructure-as-code reveals misconfigurations that allow attackers to bypass network controls and access sensitive data before deployment.
Small businesses often ignore how metadata in routine emails transforms harmless notes into high-value targets for identity theft campaigns.
Most security metrics fail because they measure effort rather than risk, creating data that looks active but hides the actual exposure of your systems.
Abandoned cloud assets create invisible attack surfaces that drain budgets and expose data long after the original project ends.
Automated scraping bypasses standard login walls by rotating residential IPs, making traditional firewall rules ineffective against modern data theft.
Most breaches fail because teams argue over who speaks, not because the data was stolen. A pre-approved message hierarchy stops that chaos before it starts.
Version control history retains deleted secrets forever, and environment variables often fail to protect credentials from memory dumps or process listings.
Small companies face the same strict 72-hour reporting deadline for data breaches as global corporations, regardless of their size or budget constraints.
Spyware hides in plain sight by using legitimate system tools, making standard antivirus scans insufficient for detecting advanced surveillance attacks.
Antivirus software relies on signature matching and behavior analysis, but it cannot stop attacks that exploit legitimate system functions without malicious code.
Small configuration errors in DNS and certificate management allow attackers to mirror your site and steal credentials without triggering standard alerts.